


Database Security Market
Database Security Market Size, Share, Insights, Competitive Landscape, and Forecast 2026 to 2033
Database Security Market Size and Trend Analysis
How Big Is the Database Security Market in 2026?
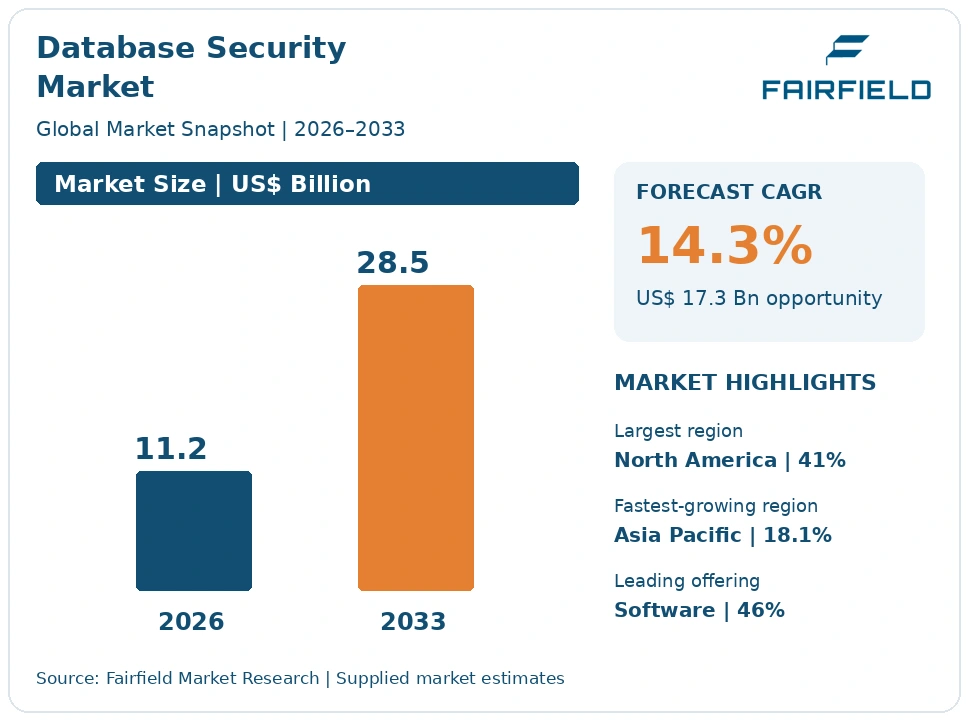
The global Database Security market size is expected to be valued at US$ 11.2 billion in 2026 and projected to reach US$ 28.5 billion by 2033, growing at a CAGR of 14.3% between 2026 and 2033.
Between 2020 and 2025 the data-layer security segment expanded at roughly a 12.8% compound rate, slower than the forecast pace, because spending stayed concentrated in classical monitoring of on-premise relational systems. Three factors lift the curve from 2026. Auditors now test stored-data controls directly under PCI DSS v4.0, so encryption and masking evidence has become a pass-or-fail item. Enterprises have lost track of where regulated records sit across managed cloud data services, which pulls budget toward discovery and posture tooling. Generative AI pipelines add urgency, because models cannot be fed data that nobody has classified. The direction is steady double-digit growth, led by cloud-delivered controls rather than appliances.
Key Report Takeaways
- By Offering, Software held 46% share in 2026, while Cloud Services is projected to expand at a 17.5% CAGR through 2033, as buyers prefer consumption-based controls that follow workloads into managed database platforms.
- By Security Control, Encryption, Tokenisation and Key Management held 24% share in 2026, while Data Security Posture Management is projected to expand at a 22.4% CAGR, reflecting the inventory gap across sprawling cloud data estates.
- By Deployment Environment, On-Premise Relational Databases held 38% share in 2026, while Cloud-Hosted and Database-as-a-Service is projected to expand at an 18.9% CAGR, driven by shared-responsibility obligations that providers do not cover.
- By End-Use Industry, BFSI held 29% share in 2026, while Healthcare and Life Sciences is projected to expand at a 16.8% CAGR, as proposed HIPAA Security Rule changes tighten encryption and asset inventory expectations.
- By Geography, North America held 41% share in 2026, while Asia Pacific is projected to expand at an 18.1% CAGR, supported by India’s Digital Personal Data Protection Act and comparable national statutes across the region.
Global Database Security Market Trends and Insights
Drivers Impact Analysis
Two forces account for most of the incremental spending on data-layer controls through 2033.
| Driver | Impact on CAGR Forecast | Geographic Relevance | Impact Timeline |
| Audit testing of stored-data controls under payment and privacy rules | High | Global, strongest in North America and Europe | Short term ≤2 years |
| Generative AI projects requiring sensitive data to be located and classified first | High | Global | Medium term 2–4 years |
Audit Testing of Stored Account Data Converts Database Security Into a Compliance Purchase
Most database security budget is released by auditors, not by security architects. PCI DSS v4.0 requires organisations to render stored account data unreadable and to justify every retention decision, and its phased, future-dated requirements raised the evidence bar further. The GDPR security-of-processing obligation names pseudonymisation and encryption explicitly, which gives European assessors a direct hook into database configuration. Buyers therefore purchase under pressure rather than conviction.
The causal chain is simple. An assessor asks where cardholder or personal records live, who queried them last quarter, and how the keys are managed. Answering that needs discovery, activity logging and key management working together, which is a tooling purchase. The Payment Card Industry Security Standards Council maintains the first standard, while ISO/IEC 27001 and ISO/IEC 27701 certification audits ask similar questions of the same systems.
Generative AI Pipelines Force Enterprises to Classify Data Before It Reaches a Model
Generative AI has created the first genuinely new reason to buy data-layer controls in a decade. Before a retrieval pipeline or a fine-tuning job touches a corporate warehouse, somebody must confirm that it will not ingest payroll records, clinical notes or payment data. That confirmation requires accurate discovery and classification across structured and semi-structured stores, which most enterprises never completed.
The mechanism runs through project approval. AI programmes are sponsored at board level and move quickly, so a blocked data access request escalates fast and gets funded. Security teams respond by deploying classification and masking so that synthetic or redacted copies can be released instead of production tables. NIST SP 800-53 control families on media protection and access enforcement give architects a recognised framework to justify the spend, and vendors have repositioned classification engines as AI-readiness tooling.
Restraints Impact Analysis
Two structural frictions hold adoption below what regulatory pressure alone would suggest.
| Restraint | Impact on CAGR Forecast | Geographic Relevance | Impact Timeline |
| Query latency and database administrator resistance to inline controls | Medium | Global | Medium term 2–4 years |
| Classification inaccuracy and tool sprawl across heterogeneous estates | High | Global, acute in large enterprises | Long term ≥4 years |
Query Latency and Database Administrator Resistance Slow Activity Monitoring Rollouts
Database activity monitoring and inline firewalls are frequently deployed in a reduced mode because they slow production systems. Agents that inspect every statement consume processor cycles on the same host that serves the application, and a transactional system running near capacity cannot absorb that. Deployments are therefore narrowed to a handful of crown-jewel instances, which caps licence expansion.
The underlying cost is operational, not purchase price. Database administrators own service-level commitments and are measured on query response, so they resist anything that adds milliseconds to a hot path. Tuning an agent to avoid that overhead takes weeks of joint work between security and database teams, and that labour is scarce. Many organisations settle for native database audit logs shipped to a collector, a weaker control that satisfies the auditor while leaving real-time blocking unused.
Inaccurate Classification and Tool Sprawl Across Mixed Estates Stall Coverage Expansion
Coverage stalls because classification accuracy collapses at enterprise scale. Pattern-based scanners flag test strings, archived tables and free-text fields as regulated data, and the resulting false positives bury the findings that matter. Teams lose confidence in the inventory, stop acting on it, and the renewal conversation becomes difficult.
The cause is estate heterogeneity. A typical large enterprise runs relational systems, document stores, a cloud warehouse, several data lakes and dozens of managed database instances, each with different logging formats and privilege models. No single product covers all of them well, so buyers assemble three or four overlapping tools and pay integration costs. Shared-responsibility confusion compounds this: teams assume the managed database provider handles encryption, auditing and configuration hardening, when the provider secures only the platform beneath the data.
Market Opportunities
Data Security Posture Management Across Cloud Data Estates Opens a Greenfield Licence Pool
Data security posture management is the clearest unclaimed revenue pool in the data layer, because it sells to organisations that already bought monitoring and still cannot answer basic inventory questions. The product scans cloud accounts for data stores nobody registered, scores their exposure, and tracks drift. It is sold as a new line item rather than a replacement, which protects existing budget.
Cloud-first enterprises and regulated digital businesses create the demand, particularly where engineering teams can create a managed database with a single command. Platform vendors, cloud-native specialists and data management firms are all building toward the same capability, and the winning pitch is accurate discovery with low false positives. Data residency and cross-border transfer rules sharpen the need, since an unregistered replica in the wrong jurisdiction is a reportable failure.
Managed Database Security Services for Mid-Market Firms Under New National Privacy Laws
Managed and co-managed database security services open a revenue pool among mid-market organisations that now face national data protection statutes but cannot staff a data security team. These buyers need monitoring, key custody and compliance reporting delivered as an outcome, priced per database rather than per licence, with evidence packaged for the regulator.
Regional service providers, systems integrators and cloud managed service firms are best placed to capture this, because the work is operational rather than product-led. Demand is concentrated in healthcare networks, regional banks, insurers and e-commerce operators in markets implementing laws such as India’s Digital Personal Data Protection Act. Supporting this shift, encryption and key management are increasingly consumed as cloud services, which removes the hardware barrier that previously kept smaller organisations out of the market entirely.
Segment Analysis
By Offering: Software Leads the Installed Base While Cloud Services Scale Fastest
Software led the offering mix with 46% share in 2026, because the core controls — activity monitoring, masking, classification and audit reporting — are bought as licensed platforms that sit alongside existing database estates. Perpetual and subscription software also fits how enterprises already budget for database tooling. Cloud Services is the fastest-growing offering at a 17.5% CAGR through 2033, as encryption, key management and posture scanning move to consumption pricing that follows workloads into managed data platforms. Appliances continue to serve high-throughput payment environments where inline inspection must run on dedicated hardware, while managed and professional services grow steadily on implementation and tuning work. The business implication is a revenue mix shifting toward recurring contracts, which lowers deal size but improves retention and gives vendors visibility into actual deployment coverage rather than shelfware.
By Security Control: Encryption Holds the Largest Share as Posture Management Accelerates
Encryption, Tokenisation and Key Management held the largest control share at 24% in 2026, because it is the control auditors test first and the one named directly in payment and privacy rules. Tokenisation is entrenched in card environments, and key management has become the hinge for cross-border data arrangements. Data Security Posture Management is the fastest-growing control at a 22.4% CAGR, expanding from a near-zero base because enterprises cannot inventory their own cloud data stores. Database activity monitoring remains a large and stable category, now feeding posture tooling rather than standing alone. Data masking and test data management grow on the back of AI and outsourced development, while database vulnerability assessment, firewalls and audit reporting hold steady compliance-driven demand. Vendors are consolidating these controls into single consoles, since buyers resist managing four separate data security products.
By Deployment Environment: On-Premise Relational Systems Dominate While Database-as-a-Service Surges
On-Premise Relational Databases retained 38% share in 2026, because the systems holding core banking ledgers, claims data and enterprise resource planning records remain on controlled infrastructure with mature monitoring already installed. These environments renew reliably but add little new spending. Cloud-Hosted and Database-as-a-Service environments form the fastest-growing category at an 18.9% CAGR, driven by the volume of managed instances created by engineering teams and by the shared-responsibility gap that leaves data-layer controls to the customer. Data warehouses and data lakes grow strongly as analytics estates concentrate sensitive records in one queryable place, making them an attractive target. NoSQL and non-relational stores remain under-protected because their native audit capabilities are thinner. The practical implication is that vendors without credible coverage of managed cloud database platforms will lose relevance regardless of their on-premise strength.
By End-Use Industry: BFSI Anchors Demand While Healthcare Records the Steepest Growth
BFSI anchored demand with 29% share in 2026, because banks, insurers and payment processors operate under the strictest stored-data rules and run the largest regulated database estates. Card environments alone justify tokenisation and inline monitoring at scale. Healthcare and Life Sciences is the fastest-growing industry at a 16.8% CAGR, as proposed modernisation of the HIPAA Security Rule would tighten encryption and asset inventory expectations, and as clinical research data moves into cloud warehouses. Government and defence buyers follow NIST SP 800-53 control baselines and sustain steady appliance and software demand. Retail and e-commerce invest where payment and loyalty data meet, while manufacturing and energy lag because their crown jewels are engineering rather than personal data. For vendors, the implication is that database compliance reporting tailored to specific regulators now outranks generic feature breadth.
Geography Analysis
Which Region Leads the Database Security Market?
North America leads the database security market with 41% share in 2026 and is forecast to grow at a 12.6% CAGR through 2033. The United States drives most of this, because its combination of payment card enforcement, state privacy statutes and sector regulators creates overlapping audit obligations on the same database estates. Large financial institutions, healthcare networks and technology firms maintain dedicated data security teams, which supports higher-touch products such as inline firewalls and enterprise key management. Canada contributes steady public sector and banking demand. Growth is slower than the global average because penetration is already high and renewals dominate new logos. The main change underway is budget migration from on-premise monitoring toward posture management, as organisations discover how many managed database instances their engineering teams created without registration.
Europe Converts Privacy Enforcement Into Encryption and Pseudonymisation Mandates
Europe held 26% share in 2026 and is forecast to grow at a 13.4% CAGR, supported by the GDPR security-of-processing obligation, which names pseudonymisation and encryption as expected safeguards. Germany, the United Kingdom, France and the Netherlands account for most spending, led by banking, insurance and public health bodies. Supervisory authorities examine technical measures during investigations, so organisations invest in demonstrable controls rather than policy documents. Data residency and cross-border transfer rules push multinationals toward customer-controlled key management, which is a premium product line. ISO/IEC 27001 and ISO/IEC 27701 certification cycles create predictable procurement windows. The regional barrier is procurement length in the public sector. The opportunity lies in sovereign cloud arrangements, where encryption key custody is the mechanism that makes managed database services acceptable to regulated buyers.
Which Region Is Growing Fastest in the Database Security Market?
Asia Pacific is growing fastest in the database security market, at an 18.1% CAGR through 2033 from 23% share in 2026. India, Japan, China, Australia and Singapore supply most of the momentum. India’s Digital Personal Data Protection Act and comparable national data protection laws elsewhere in the region have given boards a statutory reason to fund data-layer controls for the first time, and financial sector regulators have added their own audit and localisation expectations. Digital banking, insurance and public digital identity programmes have built very large database estates quickly, often on managed cloud platforms, so discovery and posture tooling is being bought alongside basic monitoring rather than after it. Price sensitivity remains real, which favours subscription and managed service delivery over appliance purchases and keeps average contract values below Western levels.
Latin America Builds Database Controls Around Payment Compliance and Banking Supervision
Latin America accounted for 5% share in 2026 and is forecast to grow at a 14.5% CAGR. Brazil leads, where the national data protection law and an active banking supervisor have pushed financial institutions to formalise database auditing, with Mexico, Chile and Colombia following. Payment modernisation has expanded card and account data volumes sharply, making PCI DSS v4.0 the practical entry point for most programmes. The principal barriers are constrained security budgets, a shallow pool of specialists who understand both database administration and security, and currency exposure on dollar-denominated licences. Adoption therefore concentrates in large banks, retailers and telecom operators. The change worth watching is the growth of regional managed security providers, which package monitoring and compliance reporting at price points mid-market firms can actually approve.
Middle East & Africa Ties Data-Layer Security to Government Digital Programmes
Middle East & Africa represented 5% share in 2026, with a forecast 15.0% CAGR. The United Arab Emirates, Saudi Arabia, Qatar and South Africa generate most demand, driven by national digital government programmes and by data protection laws that require personal records to stay within national borders. Sovereign cloud regions have been built specifically to satisfy those rules, and encryption with locally held keys is the control that makes them workable. Banking and oil and gas operators are the earliest enterprise buyers. Barriers include thin local skills, heavy dependence on systems integrators, and uneven enforcement outside the leading markets, which weakens the audit pressure that drives purchases elsewhere. The emerging opportunity is in regulated healthcare and government record systems, where classification projects precede any analytics or AI deployment.
Competitive Landscape
The database security market is moderately concentrated. A small group of platform vendors — notably IBM Corporation, Oracle Corporation, Microsoft Corporation and Thales Group — holds a substantial combined share, because activity monitoring, encryption and key management were first sold as enterprise infrastructure and renew on long cycles. Below them sits a wide field of specialists in classification, masking, posture management and privileged access to data stores. Consolidation has been steady rather than dramatic: database firewall and monitoring specialists have generally been absorbed into larger data protection portfolios, while independent posture management and classification firms continue to enter.
Vendors compete on four things that buyers test during evaluation. The first is breadth of database coverage, including document stores, cloud warehouses and managed services, not only the major relational engines. The second is classification accuracy, measured by false positive rate, because an inventory nobody trusts is worthless. The third is performance overhead, which database administrators measure directly. The fourth is the quality of audit-ready reporting mapped to PCI DSS v4.0, the GDPR, ISO/IEC 27001 and NIST SP 800-53. New entrants have come almost entirely from the cloud-native side, arriving with agentless scanning and no appliance heritage.
Strategically, the field is converging on a single console that spans discovery, classification, posture, monitoring and masking across hybrid estates. Encryption and key management vendors are extending toward posture scanning, while posture specialists add enforcement. Cloud and database platform providers bundle native controls, which commoditises basic auditing and pushes independents toward cross-platform coverage as their defensible ground. The second theme is AI readiness, with vendors positioning classification as the prerequisite for safe model deployment, and the third is packaging for managed service delivery to reach mid-market buyers.
Database Security Industry Leaders
- IBM Corporation
- Oracle Corporation
- Microsoft Corporation
- Thales Group
- Varonis Systems, Inc.
Recent Industry Developments
March 2024: PCI DSS v3.2.1 was formally retired, leaving PCI DSS v4.0 as the only active version of the payment card standard – stored account data and database logging requirements became the baseline for every assessed organisation.
June 2024: The Payment Card Industry Security Standards Council published PCI DSS v4.0.1, a limited revision clarifying requirement wording – it removed ambiguity that assessors and vendors had interpreted inconsistently for database controls.
January 2025: The United States Department of Health and Human Services issued a proposed rule to modernise the HIPAA Security Rule, including tighter encryption and asset inventory expectations – it signalled that healthcare database estates would face prescriptive technical controls.
March 2025: The future-dated requirements of PCI DSS v4.0 became mandatory rather than best practice – this converted several stored-data and monitoring controls into pass-or-fail assessment items.
October 2025: The transition period from ISO/IEC 27001:2013 to ISO/IEC 27001:2022 closed – certified organisations had to evidence updated information security controls, including those covering data handling and logging.
Database Security Market Report Scope
| Metric | Value |
| Study Period | 2020–2033 |
| Market Size 2026 | US$ 11.2 Billion |
| Market Size 2033 | US$ 28.5 Billion |
| CAGR 2026–2033 | 14.3% |
| Absolute Dollar Opportunity | US$ 17.3 Billion |
| Largest Market | North America (41% share in 2026) |
| Fastest-Growing Market | Asia Pacific (18.1% CAGR) |
| Market Concentration | Medium |
| Major Players | IBM Corporation, Oracle Corporation, Microsoft Corporation, Thales Group |
This report covers security tooling built specifically for the data layer: database activity monitoring, discovery and classification, encryption, tokenisation and key management, masking, vulnerability assessment, database firewalls, posture management and compliance reporting. General network, endpoint and workforce identity security are excluded. It is the data-layer slice of the wider cybersecurity market, which is examined separately. The base year is 2025 and the forecast period runs from 2026 to 2033 in US$ Billion.
Database Security Market Segmentation
Offering
- Software
- Appliances
- Cloud Services
- Managed and Professional Services
Security Control
- Database Activity Monitoring
- Data Discovery and Classification
- Encryption, Tokenisation and Key Management
- Data Masking and Test Data Management
- Database Vulnerability Assessment and Configuration Hardening
- Database Firewalls and Privileged Access Control
- Data Security Posture Management
- Database Audit and Compliance Reporting
Deployment Environment
- On-Premise Relational Databases
- Cloud-Hosted and Database-as-a-Service
- Data Warehouses and Data Lakes
- NoSQL and Non-Relational Stores
End-Use Industry
- BFSI
- Healthcare and Life Sciences
- Government and Defence
- IT and Telecom
- Retail and E-commerce
- Manufacturing
- Energy and Utilities
Regions
- North America
- Europe
- Asia Pacific
- Latin America
- Middle East & Africa
- Executive Summary
- Global Database Security Market Snapshot
- Future Projections
- Key Report Takeaways
- Regional Snapshot
- Market Overview
- Market Definition and Report Scope
- Historical Trends 2020–2025
- Market Dynamics
- Drivers
- Audit Testing of Stored Account Data Converts Database Security Into a Compliance Purchase
- Generative AI Pipelines Force Enterprises to Classify Data Before It Reaches a Model
- Restraints
- Query Latency and Database Administrator Resistance Slow Activity Monitoring Rollouts
- Inaccurate Classification and Tool Sprawl Across Mixed Estates Stall Coverage Expansion
- Market Opportunities
- Data Security Posture Management Across Cloud Data Estates Opens a Greenfield Licence Pool
- Managed Database Security Services for Mid-Market Firms Under New National Privacy Laws
- Drivers
- Global Database Security Market Outlook, 2020–2033
- Global Database Security Market Outlook, by Offering, Value (US$ Billion), 2020–2033
- Software
- Appliances
- Cloud Services
- Managed and Professional Services
- Global Database Security Market Outlook, by Security Control, Value (US$ Billion), 2020–2033
- Database Activity Monitoring
- Data Discovery and Classification
- Encryption, Tokenisation and Key Management
- Data Masking and Test Data Management
- Database Vulnerability Assessment and Configuration Hardening
- Database Firewalls and Privileged Access Control
- Data Security Posture Management
- Database Audit and Compliance Reporting
- Global Database Security Market Outlook, by Deployment Environment, Value (US$ Billion), 2020–2033
- On-Premise Relational Databases
- Cloud-Hosted and Database-as-a-Service
- Data Warehouses and Data Lakes
- NoSQL and Non-Relational Stores
- Global Database Security Market Outlook, by End-Use Industry, Value (US$ Billion), 2020–2033
- BFSI
- Healthcare and Life Sciences
- Government and Defence
- IT and Telecom
- Retail and E-commerce
- Manufacturing
- Energy and Utilities
- Global Database Security Market Outlook, by Region, Value (US$ Billion), 2020–2033
- North America
- Europe
- Asia Pacific
- Latin America
- Middle East & Africa
- Global Database Security Market Outlook, by Offering, Value (US$ Billion), 2020–2033
- North America Database Security Market Outlook, 2020–2033
- North America Database Security Market Outlook, by Offering, Value (US$ Billion), 2020–2033
- Software
- Appliances
- Cloud Services
- Managed and Professional Services
- North America Database Security Market Outlook, by Security Control, Value (US$ Billion), 2020–2033
- Database Activity Monitoring
- Data Discovery and Classification
- Encryption, Tokenisation and Key Management
- Data Masking and Test Data Management
- Database Vulnerability Assessment and Configuration Hardening
- Database Firewalls and Privileged Access Control
- Data Security Posture Management
- Database Audit and Compliance Reporting
- North America Database Security Market Outlook, by Deployment Environment, Value (US$ Billion), 2020–2033
- On-Premise Relational Databases
- Cloud-Hosted and Database-as-a-Service
- Data Warehouses and Data Lakes
- NoSQL and Non-Relational Stores
- North America Database Security Market Outlook, by End-Use Industry, Value (US$ Billion), 2020–2033
- BFSI
- Healthcare and Life Sciences
- Government and Defence
- IT and Telecom
- Retail and E-commerce
- Manufacturing
- Energy and Utilities
- North America Database Security Market Outlook, by Country, Value (US$ Billion), 2020–2033
- United States Database Security Market Outlook, by Offering, 2020–2033
- United States Database Security Market Outlook, by Security Control, 2020–2033
- United States Database Security Market Outlook, by Deployment Environment, 2020–2033
- United States Database Security Market Outlook, by End-Use Industry, 2020–2033
- Canada Database Security Market Outlook, by Offering, 2020–2033
- Canada Database Security Market Outlook, by Security Control, 2020–2033
- Canada Database Security Market Outlook, by Deployment Environment, 2020–2033
- Canada Database Security Market Outlook, by End-Use Industry, 2020–2033
- North America Database Security Market Outlook, by Offering, Value (US$ Billion), 2020–2033
- Europe Database Security Market Outlook, 2020–2033
- Europe Database Security Market Outlook, by Offering, Value (US$ Billion), 2020–2033
- Software
- Appliances
- Cloud Services
- Managed and Professional Services
- Europe Database Security Market Outlook, by Security Control, Value (US$ Billion), 2020–2033
- Database Activity Monitoring
- Data Discovery and Classification
- Encryption, Tokenisation and Key Management
- Data Masking and Test Data Management
- Database Vulnerability Assessment and Configuration Hardening
- Database Firewalls and Privileged Access Control
- Data Security Posture Management
- Database Audit and Compliance Reporting
- Europe Database Security Market Outlook, by Deployment Environment, Value (US$ Billion), 2020–2033
- On-Premise Relational Databases
- Cloud-Hosted and Database-as-a-Service
- Data Warehouses and Data Lakes
- NoSQL and Non-Relational Stores
- Europe Database Security Market Outlook, by End-Use Industry, Value (US$ Billion), 2020–2033
- BFSI
- Healthcare and Life Sciences
- Government and Defence
- IT and Telecom
- Retail and E-commerce
- Manufacturing
- Energy and Utilities
- Europe Database Security Market Outlook, by Country, Value (US$ Billion), 2020–2033
- Germany Database Security Market Outlook, by Offering, 2020–2033
- Germany Database Security Market Outlook, by Security Control, 2020–2033
- Germany Database Security Market Outlook, by Deployment Environment, 2020–2033
- Germany Database Security Market Outlook, by End-Use Industry, 2020–2033
- United Kingdom Database Security Market Outlook, by Offering, 2020–2033
- United Kingdom Database Security Market Outlook, by Security Control, 2020–2033
- United Kingdom Database Security Market Outlook, by Deployment Environment, 2020–2033
- United Kingdom Database Security Market Outlook, by End-Use Industry, 2020–2033
- France Database Security Market Outlook, by Offering, 2020–2033
- France Database Security Market Outlook, by Security Control, 2020–2033
- France Database Security Market Outlook, by Deployment Environment, 2020–2033
- France Database Security Market Outlook, by End-Use Industry, 2020–2033
- Netherlands Database Security Market Outlook, by Offering, 2020–2033
- Netherlands Database Security Market Outlook, by Security Control, 2020–2033
- Netherlands Database Security Market Outlook, by Deployment Environment, 2020–2033
- Netherlands Database Security Market Outlook, by End-Use Industry, 2020–2033
- Europe Database Security Market Outlook, by Offering, Value (US$ Billion), 2020–2033
- Asia Pacific Database Security Market Outlook, 2020–2033
- Asia Pacific Database Security Market Outlook, by Offering, Value (US$ Billion), 2020–2033
- Software
- Appliances
- Cloud Services
- Managed and Professional Services
- Asia Pacific Database Security Market Outlook, by Security Control, Value (US$ Billion), 2020–2033
- Database Activity Monitoring
- Data Discovery and Classification
- Encryption, Tokenisation and Key Management
- Data Masking and Test Data Management
- Database Vulnerability Assessment and Configuration Hardening
- Database Firewalls and Privileged Access Control
- Data Security Posture Management
- Database Audit and Compliance Reporting
- Asia Pacific Database Security Market Outlook, by Deployment Environment, Value (US$ Billion), 2020–2033
- On-Premise Relational Databases
- Cloud-Hosted and Database-as-a-Service
- Data Warehouses and Data Lakes
- NoSQL and Non-Relational Stores
- Asia Pacific Database Security Market Outlook, by End-Use Industry, Value (US$ Billion), 2020–2033
- BFSI
- Healthcare and Life Sciences
- Government and Defence
- IT and Telecom
- Retail and E-commerce
- Manufacturing
- Energy and Utilities
- Asia Pacific Database Security Market Outlook, by Country, Value (US$ Billion), 2020–2033
- India Database Security Market Outlook, by Offering, 2020–2033
- India Database Security Market Outlook, by Security Control, 2020–2033
- India Database Security Market Outlook, by Deployment Environment, 2020–2033
- India Database Security Market Outlook, by End-Use Industry, 2020–2033
- Japan Database Security Market Outlook, by Offering, 2020–2033
- Japan Database Security Market Outlook, by Security Control, 2020–2033
- Japan Database Security Market Outlook, by Deployment Environment, 2020–2033
- Japan Database Security Market Outlook, by End-Use Industry, 2020–2033
- China Database Security Market Outlook, by Offering, 2020–2033
- China Database Security Market Outlook, by Security Control, 2020–2033
- China Database Security Market Outlook, by Deployment Environment, 2020–2033
- China Database Security Market Outlook, by End-Use Industry, 2020–2033
- Australia Database Security Market Outlook, by Offering, 2020–2033
- Australia Database Security Market Outlook, by Security Control, 2020–2033
- Australia Database Security Market Outlook, by Deployment Environment, 2020–2033
- Australia Database Security Market Outlook, by End-Use Industry, 2020–2033
- Singapore Database Security Market Outlook, by Offering, 2020–2033
- Singapore Database Security Market Outlook, by Security Control, 2020–2033
- Singapore Database Security Market Outlook, by Deployment Environment, 2020–2033
- Singapore Database Security Market Outlook, by End-Use Industry, 2020–2033
- Asia Pacific Database Security Market Outlook, by Offering, Value (US$ Billion), 2020–2033
- Latin America Database Security Market Outlook, 2020–2033
- Latin America Database Security Market Outlook, by Offering, Value (US$ Billion), 2020–2033
- Software
- Appliances
- Cloud Services
- Managed and Professional Services
- Latin America Database Security Market Outlook, by Security Control, Value (US$ Billion), 2020–2033
- Database Activity Monitoring
- Data Discovery and Classification
- Encryption, Tokenisation and Key Management
- Data Masking and Test Data Management
- Database Vulnerability Assessment and Configuration Hardening
- Database Firewalls and Privileged Access Control
- Data Security Posture Management
- Database Audit and Compliance Reporting
- Latin America Database Security Market Outlook, by Deployment Environment, Value (US$ Billion), 2020–2033
- On-Premise Relational Databases
- Cloud-Hosted and Database-as-a-Service
- Data Warehouses and Data Lakes
- NoSQL and Non-Relational Stores
- Latin America Database Security Market Outlook, by End-Use Industry, Value (US$ Billion), 2020–2033
- BFSI
- Healthcare and Life Sciences
- Government and Defence
- IT and Telecom
- Retail and E-commerce
- Manufacturing
- Energy and Utilities
- Latin America Database Security Market Outlook, by Country, Value (US$ Billion), 2020–2033
- Brazil Database Security Market Outlook, by Offering, 2020–2033
- Brazil Database Security Market Outlook, by Security Control, 2020–2033
- Brazil Database Security Market Outlook, by Deployment Environment, 2020–2033
- Brazil Database Security Market Outlook, by End-Use Industry, 2020–2033
- Mexico Database Security Market Outlook, by Offering, 2020–2033
- Mexico Database Security Market Outlook, by Security Control, 2020–2033
- Mexico Database Security Market Outlook, by Deployment Environment, 2020–2033
- Mexico Database Security Market Outlook, by End-Use Industry, 2020–2033
- Chile Database Security Market Outlook, by Offering, 2020–2033
- Chile Database Security Market Outlook, by Security Control, 2020–2033
- Chile Database Security Market Outlook, by Deployment Environment, 2020–2033
- Chile Database Security Market Outlook, by End-Use Industry, 2020–2033
- Colombia Database Security Market Outlook, by Offering, 2020–2033
- Colombia Database Security Market Outlook, by Security Control, 2020–2033
- Colombia Database Security Market Outlook, by Deployment Environment, 2020–2033
- Colombia Database Security Market Outlook, by End-Use Industry, 2020–2033
- Latin America Database Security Market Outlook, by Offering, Value (US$ Billion), 2020–2033
- Middle East & Africa Database Security Market Outlook, 2020–2033
- Middle East & Africa Database Security Market Outlook, by Offering, Value (US$ Billion), 2020–2033
- Software
- Appliances
- Cloud Services
- Managed and Professional Services
- Middle East & Africa Database Security Market Outlook, by Security Control, Value (US$ Billion), 2020–2033
- Database Activity Monitoring
- Data Discovery and Classification
- Encryption, Tokenisation and Key Management
- Data Masking and Test Data Management
- Database Vulnerability Assessment and Configuration Hardening
- Database Firewalls and Privileged Access Control
- Data Security Posture Management
- Database Audit and Compliance Reporting
- Middle East & Africa Database Security Market Outlook, by Deployment Environment, Value (US$ Billion), 2020–2033
- On-Premise Relational Databases
- Cloud-Hosted and Database-as-a-Service
- Data Warehouses and Data Lakes
- NoSQL and Non-Relational Stores
- Middle East & Africa Database Security Market Outlook, by End-Use Industry, Value (US$ Billion), 2020–2033
- BFSI
- Healthcare and Life Sciences
- Government and Defence
- IT and Telecom
- Retail and E-commerce
- Manufacturing
- Energy and Utilities
- Middle East & Africa Database Security Market Outlook, by Country, Value (US$ Billion), 2020–2033
- United Arab Emirates Database Security Market Outlook, by Offering, 2020–2033
- United Arab Emirates Database Security Market Outlook, by Security Control, 2020–2033
- United Arab Emirates Database Security Market Outlook, by Deployment Environment, 2020–2033
- United Arab Emirates Database Security Market Outlook, by End-Use Industry, 2020–2033
- Saudi Arabia Database Security Market Outlook, by Offering, 2020–2033
- Saudi Arabia Database Security Market Outlook, by Security Control, 2020–2033
- Saudi Arabia Database Security Market Outlook, by Deployment Environment, 2020–2033
- Saudi Arabia Database Security Market Outlook, by End-Use Industry, 2020–2033
- Qatar Database Security Market Outlook, by Offering, 2020–2033
- Qatar Database Security Market Outlook, by Security Control, 2020–2033
- Qatar Database Security Market Outlook, by Deployment Environment, 2020–2033
- Qatar Database Security Market Outlook, by End-Use Industry, 2020–2033
- South Africa Database Security Market Outlook, by Offering, 2020–2033
- South Africa Database Security Market Outlook, by Security Control, 2020–2033
- South Africa Database Security Market Outlook, by Deployment Environment, 2020–2033
- South Africa Database Security Market Outlook, by End-Use Industry, 2020–2033
- Middle East & Africa Database Security Market Outlook, by Offering, Value (US$ Billion), 2020–2033
- Competitive Landscape
- Market Concentration and Industry Leaders
- Competitive Differentiation
- Strategic Moves and Market Direction
- Recent Industry Developments
- Company Profiles
- IBM Corporation
- Oracle Corporation
- Microsoft Corporation
- Thales Group
- Broadcom Inc.
- Informatica Inc.
- Varonis Systems, Inc.
- Trellix
- Fortinet, Inc.
- Protegrity
- BigID, Inc.
- Netwrix Corporation
- Perforce Software, Inc.
- Appendix
- Research Methodology
- Report Assumptions
- Acronyms and Abbreviations
Offering
- Software
- Appliances
- Cloud Services
- Managed and Professional Services
Security Control
- Database Activity Monitoring
- Data Discovery and Classification
- Encryption, Tokenisation and Key Management
- Data Masking and Test Data Management
- Database Vulnerability Assessment and Configuration Hardening
- Database Firewalls and Privileged Access Control
- Data Security Posture Management
- Database Audit and Compliance Reporting
Deployment Environment
- On-Premise Relational Databases
- Cloud-Hosted and Database-as-a-Service
- Data Warehouses and Data Lakes
- NoSQL and Non-Relational Stores
End-Use Industry
- BFSI
- Healthcare and Life Sciences
- Government and Defence
- IT and Telecom
- Retail and E-commerce
- Manufacturing
- Energy and Utilities
Regions
- North America
- Europe
- Asia Pacific
- Latin America
- Middle East & Africa
Our Research Methodology
Considering the volatility of business today, traditional approaches to strategizing a game plan can be unfruitful if not detrimental. True ambiguity is no way to determine a forecast. A myriad of predetermined factors must be accounted for such as the degree of risk involved, the magnitude of circumstances, as well as conditions or consequences that are not known or unpredictable. To circumvent binary views that cast uncertainty, the application of market research intelligence to strategically posture, move, and enable actionable outcomes is necessary.
View Methodology
Quality Assured
Rigorous Validation Process

Confidentiality Assured
End-to-end Data Security

Custom Research Services
Tailored To Your Objectives
FAQs
The database security market is valued at US$ 11.2 billion in 2026, covering data-layer controls sold as software, appliances, cloud services and managed services.
The market is projected to reach US$ 28.5 billion by 2033, growing at a 14.3% CAGR and adding US$ 17.3 billion in absolute opportunity.
Encryption, Tokenisation and Key Management holds the largest control share at 24% in 2026, because auditors test stored-data protection before any other database control.
Asia Pacific is growing fastest at an 18.1% CAGR through 2033, driven by new national data protection statutes and rapid managed cloud database adoption.
Concentration is medium: four platform vendors hold substantial combined share, while specialists in classification, masking and posture management compete across heterogeneous database estates.
Related Reports
Smart Water Management Market Size, Share, Insights, Competitive Landscape, and Forecast 2026 to 2033
Explore the smart water management market, reaching US$ 45.2 billion by 2033 at 11.0% CAGR, with solution, regional and competitive insights.
Infusion Pump Software Market Size, Share, Insights, Competitive Landscape, and Forecast 2026 to 2033
Explore the infusion pump software market, reaching US$ 2.4 billion by 2033 at 10.4% CAGR, with software, regional and competitive insights.
Smart Home Appliances Market Size, Share, Insights, Competitive Landscape, and Forecast 2026 to 2033
Explore the smart home appliances market, reaching US$ 113.0 billion by 2033 at 13.0% CAGR, with product, regional and competitive insights.
Smart Cities Market Size, Share, Insights, Competitive Landscape, and Forecast 2026 to 2033
Explore the smart cities market, reaching US$ 420.0 billion by 2033 at 12.7% CAGR, with solution, regional and competitive insights.
Industrial Robotics Market Size, Share, Insights, Competitive Landscape, and Forecast 2026 to 2033
Explore the industrial robotics market, reaching US$ 95.0 billion by 2033 at 8.4% CAGR, with robot types, regional and competitive insights.
Holographic Display Market Size, Share, Insights, Competitive Landscape, and Forecast 2026 to 2033
Explore the holographic display market, reaching US$ 7.6 billion by 2033 at 17.9% CAGR, with technology, regional and competitive insights.